Sponsored LinkedIn post
A dedicated post to introduce your brand to my audience.
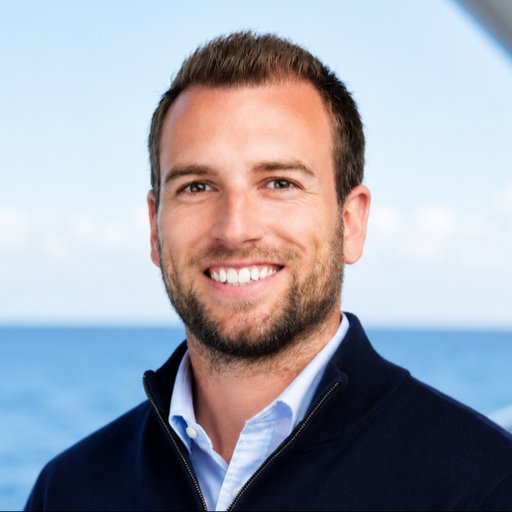
Head of Sales & Growth @ CIS Limited
Companies pay Nick to write a post about their product on LinkedIn.
This page is where they book it. Below: Nick's audience, recent posts and price. Naano, the platform behind this page, handles the brief, your approval of the post and the payment.
€63per post, fixed price
You approve the post before it goes live
Looking for Nick? View LinkedIn profileA creator yourself? Create your own page
Your IT Is My Problem Now | Managed IT & Cyber for SMEs | Risk Owned, Not Just Managed | CIS
Most IT companies sell you a service. They monitor some things. Fix stuff when it breaks. Send you a bill. Nobody actually owns the outcome. That’s what I set out to change. I kept seeing the same thing: providers hitting every target on the contract while the client still got hacked, still lost a morning to email, still failed the audit. The numbers looked fine. The business didn’t. Once you’ve watched that gap open up a few times, “we met our SLA” stops being an acceptable answer. So at CIS we do it differently. We take contractual accountability for your IT. Not response times. Actual ownership of the result. If something isn’t working, that’s on us. Properly on us. We work with UK SMEs, 20 to 200+ staff: professional services, legal, accountancy, healthcare, manufacturing. The kind of business where downtime costs real money and a breach ends careers. Your last IT provider probably hit their SLAs. You still got hacked. Or your finance team still lost half a day to Outlook. Or your auditor still flagged something nobody fixed. SLAs aren’t outcomes. We own outcomes. Credentials, briefly: 35+ years. Microsoft Gold Partner. Sophos Partner. Cyber Essentials Plus. ISO27001. G-Cloud 15 Supplier. But the bit that matters: your IT becomes my problem. Not yours. If you’re tired of chasing your IT provider, drop me a message. I’ll tell you straight if we’re a fit. If we’re not, I’ll point you to someone who is. Worst case, you get an honest answer and a better direction than you walked in with.
Public LinkedIn data · Sep 18, 2026
Nick Shaw
SpaceX didn't design the clean engine. They flew the ugly one until it told them what to remove.. Most of the sales and marketing I see in SME world never gets to the ugly version. The website's been "in redesign" since last spring. The outbound campaign is waiting on the perfect ICP. The case study is waiting on a client to sign off a quote they'll never read again. Nothing ships, so nothing gets tested, so nothing gets better, and the whole thing quietly dies in a folder. I've built my entire sales function at CIS this way. The first version of our outbound was rough. Sequences I'd be embarrassed to show you now, a list I put together by hand, a pitch that changed every fortnight because prospects kept correcting me on what actually mattered to them. It went out anyway. Every reply taught me something no planning meeting ever would have, and the version running today is nothing like what I'd have designed on paper. That's the bit people miss about the photo. All those pipes on the left engine are there because nobody knew yet which ones were unnecessary. You don't find that out in CAD. You find it out by lighting the thing and seeing what melts. Polish is a reaction to real feedback, not a substitute for it. If something's been sat in draft for more than a month, it isn't being refined, it's being avoided. Send the rough version this week and let the market do the editing. What have you been polishing instead of shipping?
Nick Shaw
Your MSP mentions security once a year. That's not how attackers work. Almost 43% of cyberattacks target small and medium businesses. And 88% of breaches at SMBs involve ransomware, compared to 39% at large enterprises. Most of those businesses don't have anyone steering the security programme. That job lands on whoever is closest to the infrastructure. Usually the MSP. CISA's guidance for MSPs is specific about what that means in practice: 1. Contracts should spell out security roles clearly 2. Customers get visibility into logging and monitoring 3. Incidents get reported, confirmed or suspected The Australian Cyber Security Centre puts it even more directly. It says MSPs should have an upfront, transparent conversation with customers about what security they can actually expect, and keep having it. Not a slide in the onboarding deck. Not a line in the contract you hope nobody reads closely. If security only comes up at renewal time, the client has no idea what they're actually covered for the other eleven months. When did you last talk to a client about what happens if they get hit?
Nick Shaw
Most stagnation in the MSP space isn't a technology problem. It’s a conformity problem… When everyone around you sells the same per-seat model, pitches the same SLAs, and packages the exact same stack, blending in feels like safety. Diverging feels like risk. So leaders convince themselves: "Clients will only ever buy per-seat pricing." "Commoditisation is just the reality of our market." "Our value is tied to uptime and ticket counts." In psychology, when a pattern repeats long enough, familiarity gets mistaken for truth. Sticking to the consensus feels sensible because if you fail using the standard model, no one blames you. But if you try something different and stumble, the blame is yours alone. Safety in the herd is comfortable, but it's also where margins go to die. Breaking out doesn’t require revolutionising technology overnight. It starts with the quiet courage to challenge the default script. The longer an industry repeats the same assumptions, the more they start to feel like facts. Progress begins when someone tests them.
Choose a format for your next LinkedIn collaboration.
A dedicated post to introduce your brand to my audience.
Your collaboration, managed on Naano
How does this price compare? B2B creator rates 2026
Based on 45 people who reacted to or commented on my posts. Percentages use the profiles that could be classified.
Based on 45 people who reacted to or commented on my posts. Percentages use the profiles that could be classified.
Based on 45 people who reacted to or commented on my posts. Percentages use the profiles that could be classified.
Storefront by Naano · Create yours
Nick Shaw is a B2B LinkedIn creator based in the United Kingdom with 7,136 followers, posting about Software, Sales, and Cybersecurity. On Naano, one sponsored LinkedIn post by Nick Shaw costs €63, a fixed price per post.
The Naano team casts the creators, writes the briefs, reviews every draft with you and reports results per creator. You approve the shortlist and every draft.